Why ERP Security Has Become a Business-Critical Responsibility
Enterprise Resource Planning (ERP) systems have become central to how modern organizations manage finance, human resources, supply chains, procurement, sales, and operations. Because these SAP Security GRC Course in Chennai platforms store and process large volumes of sensitive business information, protecting them is no longer only an IT responsibility. ERP security has become a business-critical responsibility that requires cooperation between technology teams, management, employees, and other stakeholders.
1. ERP Systems Contain Valuable Business Data
ERP platforms bring important business information together in one environment. Financial records, employee information, customer details, supplier data, inventory records, and operational information may all be connected through the system. A security weakness can therefore expose multiple areas of an organization at once. Protecting ERP data helps businesses maintain confidentiality, prevent unauthorized changes, and reduce the risk of data loss.
2. Cybersecurity Threats Are Increasing
Organizations face growing risks from phishing, stolen credentials, malware, ransomware, insider threats, and unauthorized access. Attackers may target ERP environments because compromising one account or application could provide access to valuable business resources. Security teams must therefore monitor access, identify unusual activity, apply updates, and address vulnerabilities before they become serious incidents.
3. Business Operations Depend on ERP Availability
ERP security is not only about protecting information. It is also about keeping critical business operations running. If an ERP system becomes unavailable because of a cyberattack or security incident, activities such as purchasing, payroll processing, order management, inventory control, and financial reporting can be disrupted. Strong security practices can help organizations improve resilience and reduce operational downtime.
4. Access Control Reduces Security Risks
Not every employee needs access to every ERP function or piece of information. Role-based access control allows SAP Security GRC Course in Bangalore organizations to provide users with permissions appropriate to their responsibilities. Regularly reviewing user accounts, removing unnecessary privileges, implementing multi-factor authentication, and monitoring privileged accounts can reduce opportunities for unauthorized access.
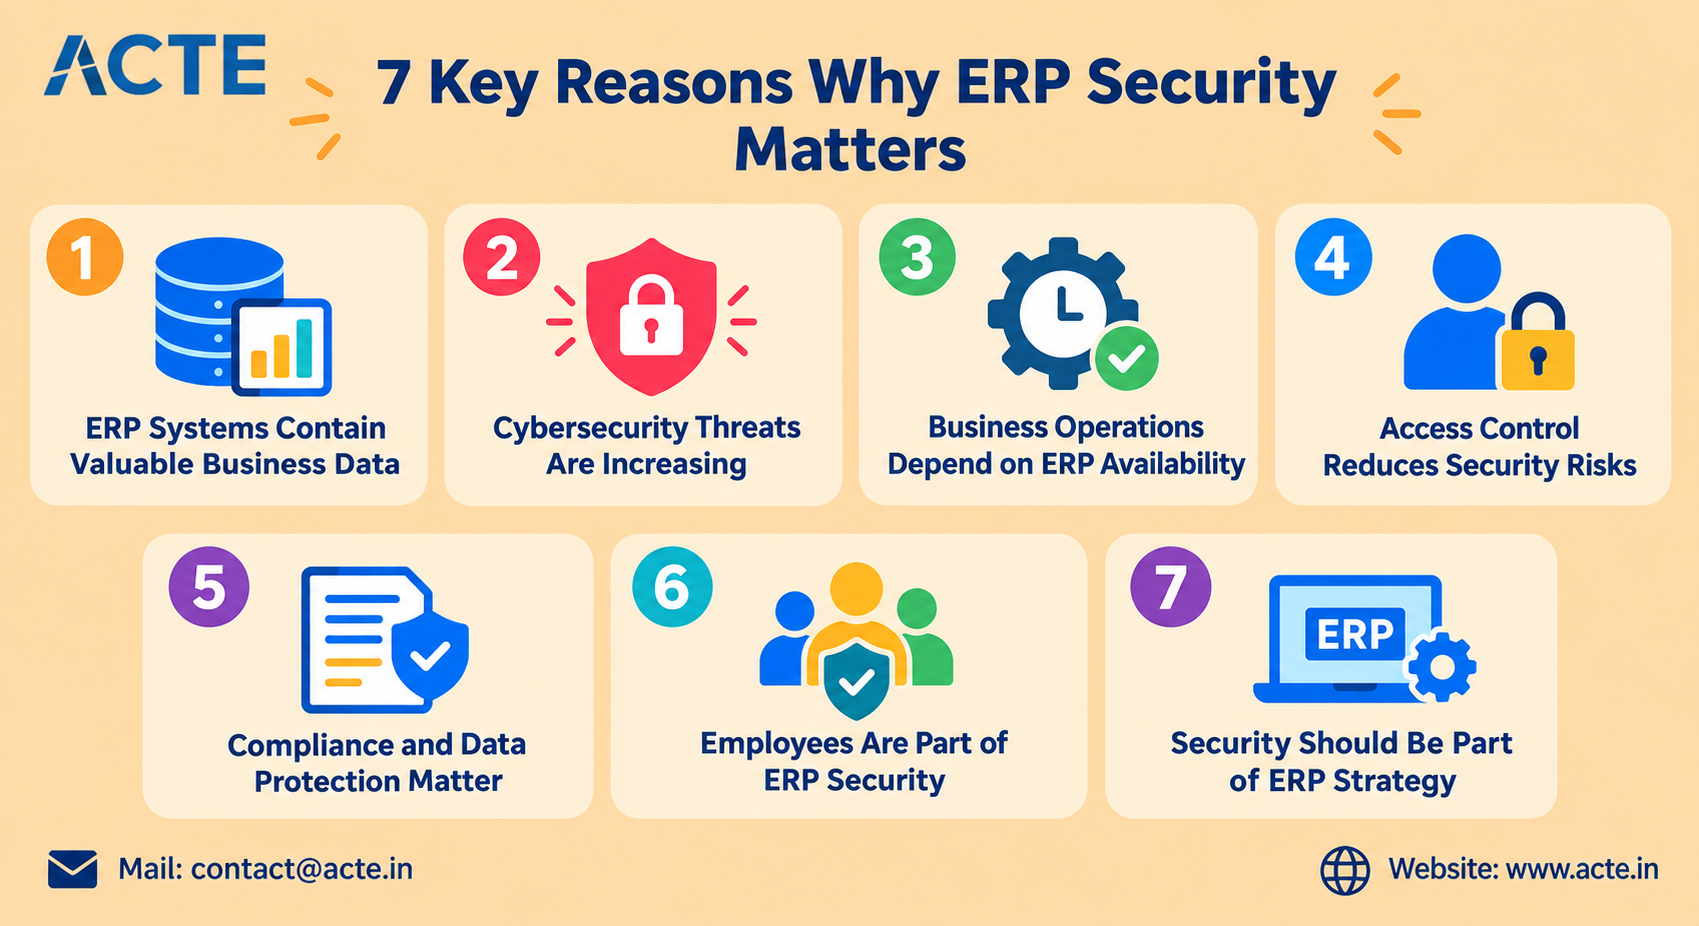
5. Compliance and Data Protection Matter
Many organizations operate under industry regulations and data protection requirements. ERP systems often contain information that must be handled carefully according to legal, contractual, or internal policies. Security controls, audit trails, access management, and appropriate data protection practices can help SAP Security GRC Course in Hyderabad organizations demonstrate responsible information management and support compliance efforts.
6. Employees Are Part of ERP Security
Technology alone cannot provide complete ERP protection. Employees interact with ERP systems every day, making security awareness essential. Training employees to recognize phishing attempts, use strong authentication practices, protect credentials, and report suspicious activity can reduce risks caused by human error. Organizations should build security awareness into their regular workplace practices.
7. Security Should Be Part of ERP Strategy
ERP security works best when it is considered during implementation, upgrades, integrations, and ongoing SAP Security GRC Online Course system management rather than treated as an afterthought. Security assessments, vulnerability management, backup strategies, incident response plans, and continuous monitoring should form part of the broader ERP strategy. Business leaders should also understand how security risks could affect revenue, operations, customers, and reputation.
Conclusion
ERP security has evolved from a technical concern into a business-critical responsibility. Because ERP platforms support essential processes and contain valuable information, security failures can affect an organization's operations, finances, compliance, and reputation. By combining strong access controls, employee awareness, monitoring, regular security assessments, and strategic planning, organizations can create a more secure ERP environment and strengthen their overall business resilience.
- Digital Agency
- Literie
- Location de voitures
- Restaurant
- Restaurant
- Mode
- Mode
- Information
- Marketing
- Tourisme
- Développement
- Découverte
- Législation
- Gastronomie
- Pâtisserie
- Veranstaltung
- Art
- Causes
- Crafts
- Dance
- Drinks
- Film
- Fitness
- Food
- Spiele
- Gardening
- Health
- Startseite
- Literature
- Music
- Networking
- Andere
- Party
- Religion
- Shopping
- Sports
- Theater
- Wellness
 Deutsch
 Indian
 English
 French
 Arabic
 Spanish
 Portuguese
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek