Costly Penetration Testing Mistakes Indian BFSI Companies Keep Repeating
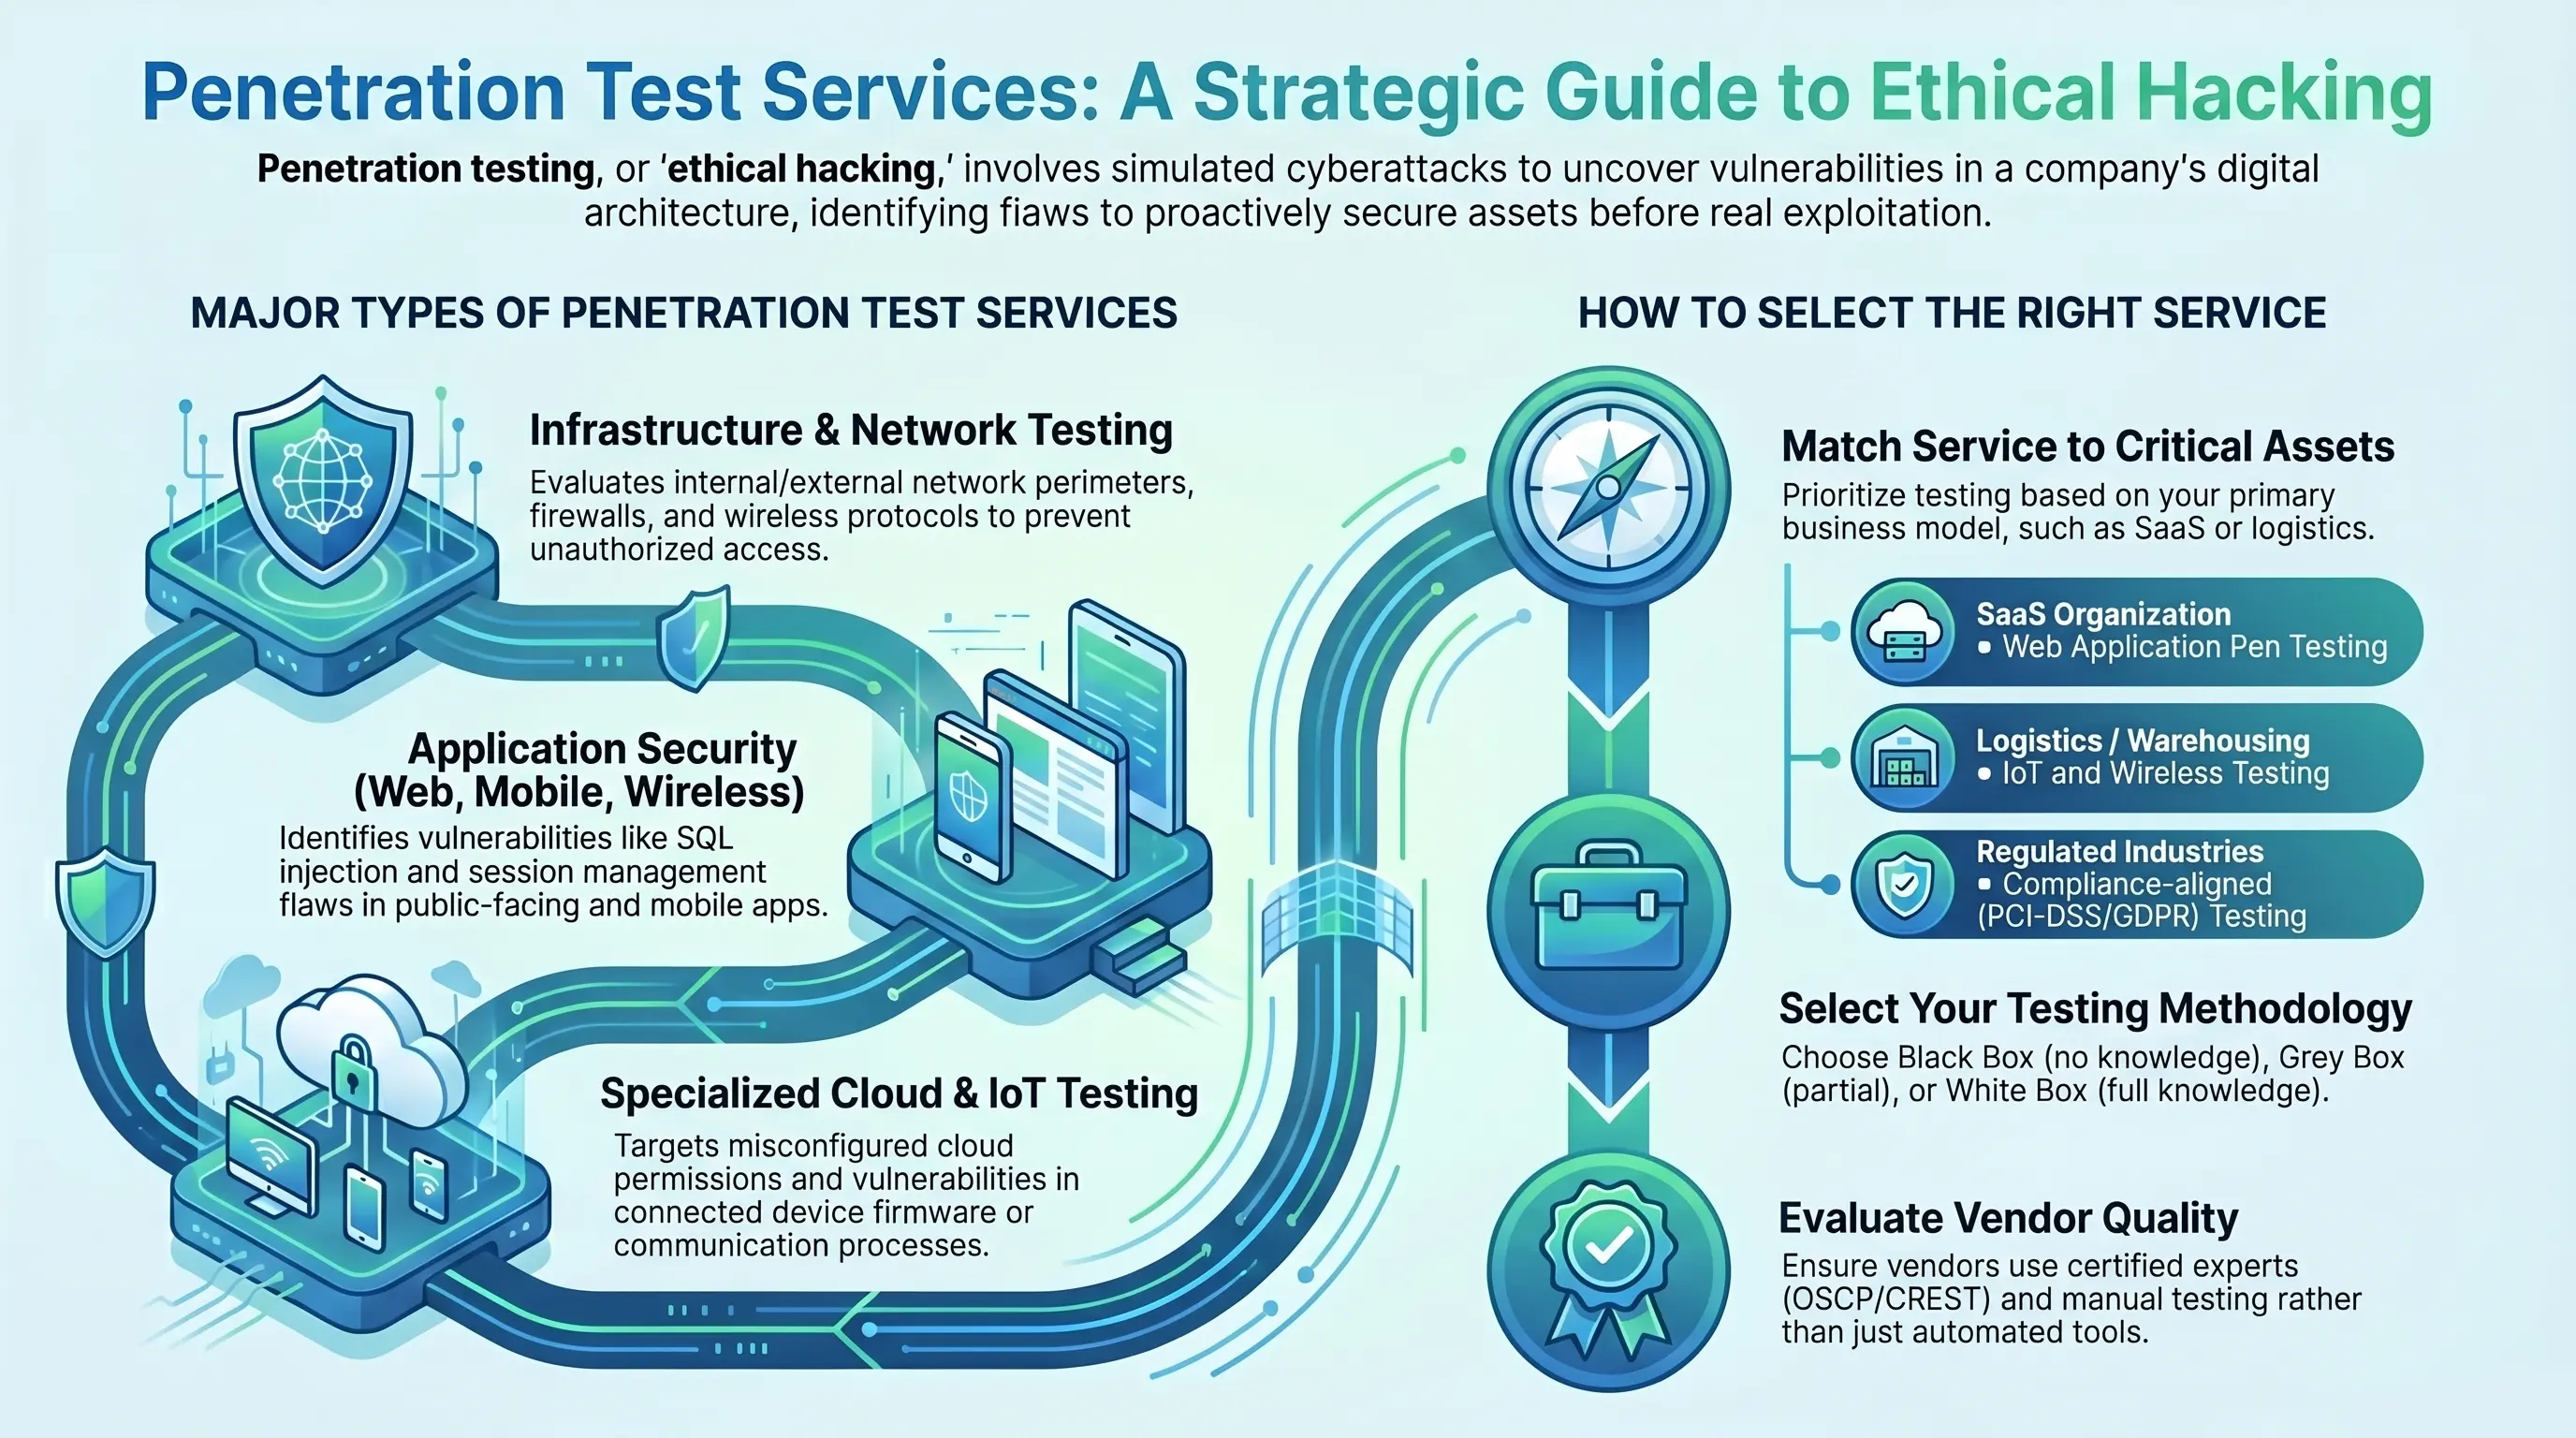
Passing an Audit Doesn't Always Mean Being Secure
It's a pattern that shows up more often than it should a BFSI company passes its compliance audit, then suffers a breach months later through a vulnerability that a proper test should have caught. The gap usually isn't a lack of effort; it's a handful of recurring mistakes in how penetration testing services get scoped, executed, or acted on. Understanding these mistakes is the first step to avoiding them.
Why BFSI Firms Are Especially Prone to These Errors
Financial institutions operate under intense regulatory pressure from the RBI, SEBI, and IRDAI, alongside CERT-In reporting mandates. That pressure sometimes pushes teams toward testing that satisfies the letter of a compliance checklist rather than genuinely probing for exploitable risk. The result is a false sense of security that only becomes obvious after an incident.
Mistake 1: Treating Testing as an Annual Formality
Many BFSI firms schedule a single VAPT engagement each year purely to satisfy audit requirements, then leave systems untested for the rest of the cycle. But new features, third-party integrations, and infrastructure changes introduce new risk continuously. A vulnerability introduced in month three can sit exposed for nine months before the next scheduled test catches it.
Mistake 2: Accepting Automated-Only Scan Reports Automated scanning tools are a useful baseline, but they cannot validate whether a flaw is truly exploitable or chain smaller issues into a serious attack path. Firms that accept scan-only reports as "penetration testing" often miss the business logic flaws that manual, certified testers are specifically trained to find.
Mistake 3: Narrow Scoping That Excludes Real Risk
It's common to scope testing around the customer-facing website while excluding internal networks, third-party vendor integrations, or mobile banking apps. Attackers don't respect those boundaries — a compromised third-party integration is just as damaging as a flaw in the primary application.
Mistake 4: Skipping Retesting After Remediation
Fixing a vulnerability and assuming it's resolved without formal retesting is a frequent and costly gap. Remediation efforts sometimes introduce new issues or fail to fully close the original flaw, and without a validation step, that failure only surfaces during an actual attack or the next scheduled audit.
Mistake 5: Choosing a Vendor Based on Price Alone
Selecting the lowest-cost provider without evaluating tester certifications or methodology often means sacrificing the depth of manual exploitation needed to find serious flaws — a costly trade-off in a sector where a single exploited vulnerability can mean direct financial loss.
A Quick Reference: Mistake vs. Correction
|
Common Mistake |
Better Practice |
|
Annual-only testing |
Quarterly or continuous testing for critical systems |
|
Automated-only reports |
Manual exploitation by certified testers |
|
Narrow scoping |
Include internal networks, APIs, and vendor integrations |
|
Skipping retesting |
Formal fix validation before closing the engagement |
|
Price-only vendor selection |
Evaluate certifications, methodology, and compliance mapping |
How to Correct Course
Fixing these mistakes starts with scoping testing around actual risk exposure rather than the minimum an auditor requires, choosing a partner who combines automated scanning with manual exploitation, and building retesting into every engagement from the start rather than treating it as optional.
Industry Use Case
A financial services organization that had previously relied on annual, scan-only testing engaged IBN Technologies for a full-scope VAPT assessment including manual exploitation across its core application and network layer. The engagement uncovered exploitable authorization flaws that prior automated-only testing had missed entirely, and remediation was verified through formal retesting.
Compliance Context
IBN Technologies delivers hybrid testing that combines automated scanning with manual exploitation by CEH, OSCP, and CISSP-certified professionals, with findings mapped to RBI, SEBI, IRDAI, and CERT-In requirements, and includes retesting and validation as part of its VAPT service tiers.
Avoiding these recurring mistakes is what separates BFSI companies that merely pass an audit from those whose penetration testing services actually protect them when it counts.
- Digital Agency
- Literie
- Location de voitures
- Restaurant
- Restaurant
- Mode
- Mode
- Information
- Marketing
- Tourisme
- Développement
- Découverte
- Législation
- Gastronomie
- Pâtisserie
- Veranstaltung
- Art
- Causes
- Crafts
- Dance
- Drinks
- Film
- Fitness
- Food
- Spiele
- Gardening
- Health
- Startseite
- Literature
- Music
- Networking
- Andere
- Party
- Religion
- Shopping
- Sports
- Theater
- Wellness
 Deutsch
 Indian
 English
 French
 Arabic
 Spanish
 Portuguese
 Turkish
 Dutch
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek