


SIEM as a Service: 8 Powerful Cybersecurity Benefits for U.S. SMEs
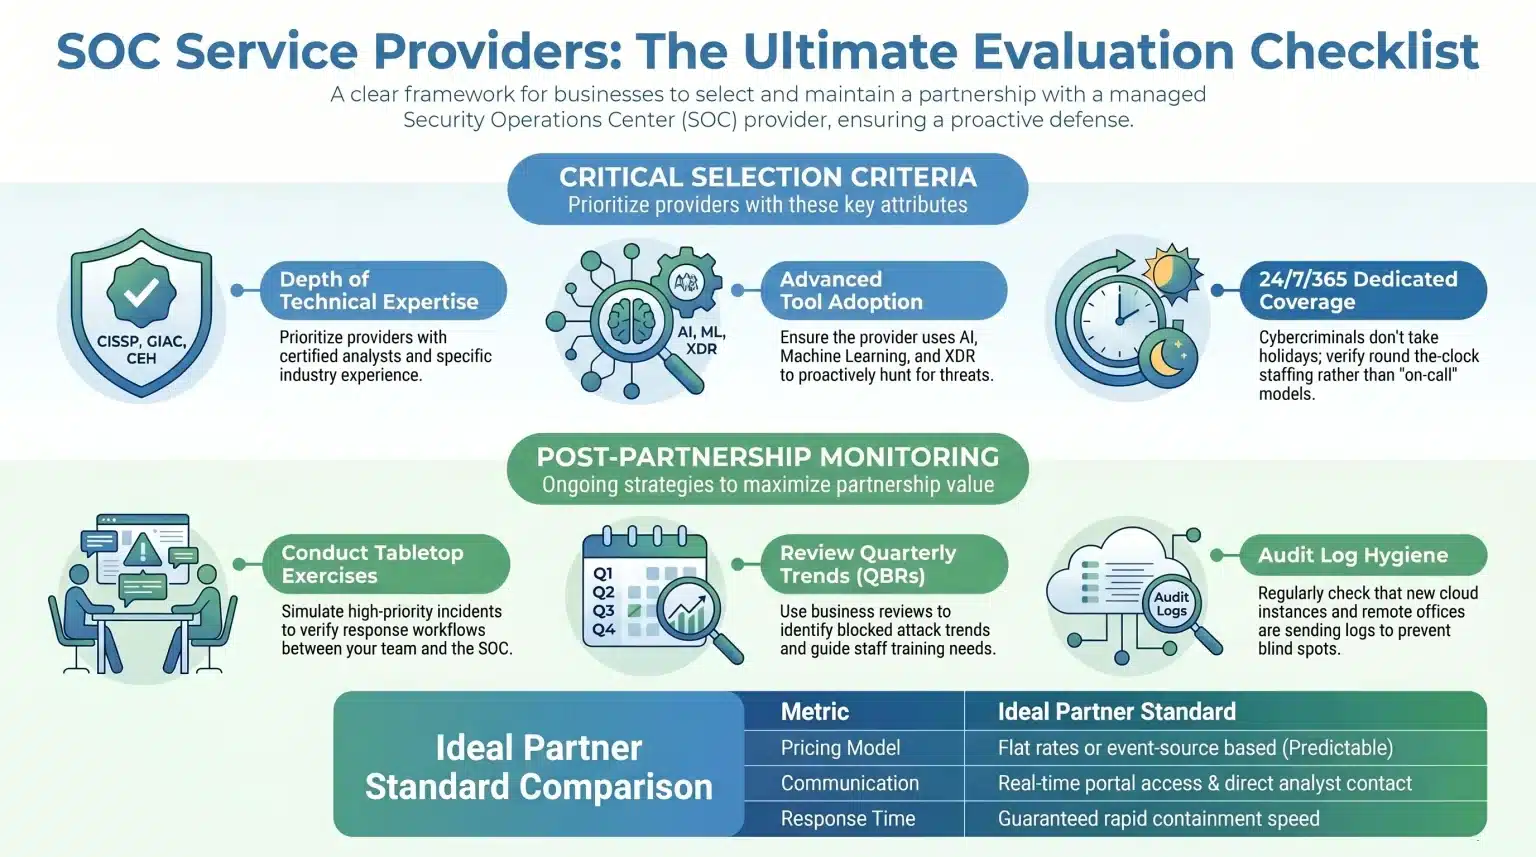
Healthcare organizations are facing an increasingly sophisticated cyber threat landscape as digital health records, cloud-based applications, and connected medical technologies become integral to patient care. Over the past year, cybercriminals have intensified ransomware campaigns, credential theft, and phishing attacks against healthcare providers because of the high value of protected health information (PHI). For U.S.-based healthcare SMEs, even a minor cybersecurity incident can interrupt patient services, compromise sensitive data, and lead to costly regulatory consequences.
To address these evolving risks, many organizations are adopting SIEM as a service to strengthen security monitoring without building a dedicated in-house security operations team. By combining centralized log management, real-time event correlation, and intelligent network threat detection, healthcare organizations gain continuous visibility into their IT environments and can identify suspicious activity before it develops into a significant security incident. This proactive approach enables healthcare SMEs to improve cyber resilience while maintaining business continuity and compliance.
Why SIEM as a Service Is Essential for Healthcare SMEs
SIEM as a service delivers cloud-based Security Information and Event Management capabilities that continuously collect, analyze, and correlate security data from networks, servers, endpoints, cloud workloads, and business applications. Instead of relying on isolated security tools, organizations receive centralized visibility into security events across their entire infrastructure.
Healthcare organizations manage complex digital ecosystems that include electronic health record platforms, patient portals, billing systems, remote access solutions, and connected medical devices. Each system generates valuable security data that must be monitored continuously to detect emerging threats.
An effective SIEM as a service solution helps healthcare organizations:
- Centralize security event monitoring.
- Improve security visibility across IT environments.
- Detect suspicious activities early.
- Prioritize critical security incidents.
- Support faster investigations.
- Strengthen cybersecurity governance.
According to the U.S. Cybersecurity and Infrastructure Security Agency (CISA), continuous monitoring and centralized visibility are essential for defending against evolving cyber threats.
Authoritative resources:
https://www.nist.gov/cyberframework
How SIEM as a Service Improves Network Threat Detection
Modern healthcare environments generate thousands of security events every day. Reviewing these events manually is impractical and often results in delayed responses.
SIEM as a service automates the collection and analysis of security logs from multiple systems while correlating events to identify patterns that may indicate malicious activity. Combined with advanced network threat detection, organizations can recognize unusual behavior such as unauthorized login attempts, abnormal network traffic, privilege escalation, and suspicious user activity before attackers achieve their objectives.
This approach enables healthcare organizations to:
- Detect threats in real time.
- Reduce attacker dwell time.
- Improve investigation efficiency.
- Prioritize high-risk incidents.
- Strengthen security monitoring.
- Support coordinated incident response.
Rather than reacting after damage has occurred, organizations can proactively address security risks as they emerge.
Business Benefits of SIEM as a Service for Healthcare Organizations
SIEM as a Service Strengthens Continuous Security Monitoring
Healthcare systems operate continuously, making around-the-clock monitoring essential. SIEM as a service provides centralized visibility into security events, helping organizations identify threats regardless of when they occur.
SIEM as a Service Improves Network Threat Detection
Advanced network threat detection enables organizations to identify malicious activity by analyzing behavior across networks, endpoints, cloud services, and applications. This helps reduce false positives while improving the accuracy of security investigations.
SIEM as a Service Accelerates Incident Response
Early threat identification allows organizations to investigate and respond more quickly. Faster response reduces operational disruption and minimizes the potential impact of cybersecurity incidents on patient care.
SIEM as a Service Enhances Compliance Readiness
Healthcare organizations are expected to maintain strong cybersecurity controls and security event records. Centralized monitoring supports documentation, security visibility, and governance activities that contribute to stronger compliance readiness.
SIEM as a Service Increases Operational Efficiency
Managing multiple disconnected security tools consumes valuable IT resources. SIEM as a service centralizes monitoring activities, enabling internal teams to focus on strategic healthcare technology initiatives while maintaining stronger cybersecurity oversight.
Common Healthcare Cybersecurity Challenges Solved by SIEM as a Service
Healthcare SMEs regularly encounter cybersecurity challenges that require continuous monitoring and rapid analysis, including:
- Ransomware attacks.
- Phishing campaigns.
- Unauthorized system access.
- Insider security risks.
- Cloud security monitoring.
- Endpoint security incidents.
- High volumes of security alerts.
- Limited cybersecurity personnel.
By implementing SIEM as a service, organizations gain centralized security intelligence that improves network threat detection while enabling more effective prioritization of cybersecurity events.
How IBN Technologies Delivers SIEM as a Service
IBN Technologies provides cybersecurity services that help organizations strengthen security operations through structured SIEM and SOC capabilities. Its cybersecurity specialists continuously monitor security events, analyze suspicious activities, and support incident response efforts that improve organizational resilience.
The company's SIEM as a service delivers centralized visibility across healthcare IT environments by collecting and analyzing security data from multiple systems. Combined with advanced network threat detection, IBN Technologies helps organizations identify suspicious behavior, investigate potential threats, and improve security decision-making before incidents affect critical operations.
IBN Technologies helps healthcare SMEs:
- Centralize security monitoring.
- Improve security event visibility.
- Detect evolving cyber threats.
- Strengthen incident response readiness.
- Support cybersecurity compliance initiatives.
- Build long-term cyber resilience.
By combining experienced cybersecurity professionals with structured SIEM methodologies, IBN Technologies enables healthcare organizations to improve operational security without increasing internal complexity.
Best Practices for Maximizing SIEM as a Service
Healthcare organizations can maximize the value of SIEM as a service by adopting several cybersecurity best practices:
- Continuously monitor security events.
- Maintain updated security policies.
- Implement strong identity and access controls.
- Review security alerts regularly.
- Conduct periodic vulnerability assessments.
- Improve employee cybersecurity awareness.
- Continuously enhance network threat detection capabilities.
- Align cybersecurity initiatives with recognized industry standards.
These practices improve organizational resilience while strengthening protection against evolving cyber threats.
Conclusion
Healthcare organizations require proactive cybersecurity strategies to defend against increasingly sophisticated attacks targeting sensitive patient information and critical business systems. By implementing SIEM as a service, U.S. healthcare SMEs gain centralized security monitoring, faster threat identification, and improved operational visibility across complex IT environments. Supported by advanced network threat detection, organizations can identify emerging risks early, reduce operational disruption, and strengthen overall cyber resilience.
IBN Technologies delivers dependable SIEM and SOC services that help healthcare organizations improve cybersecurity through centralized monitoring, intelligent threat analysis, and structured incident response support. As digital healthcare environments continue to evolve, partnering with an experienced cybersecurity provider enables organizations to strengthen security operations while maintaining business continuity and compliance.
Strengthen your healthcare cybersecurity strategy with IBN Technologies' SIEM as a service. Gain continuous monitoring, advanced network threat detection, and expert cybersecurity support to safeguard sensitive healthcare data and build a resilient security posture for the future.
- Digital Agency
- Literie
- Location de voitures
- Restaurant
- Restaurant
- Mode
- Mode
- Information
- Marketing
- Tourisme
- Développement
- Découverte
- Législation
- Gastronomie
- Pâtisserie
- Evenement
- Art
- Causes
- Crafts
- Dance
- Drinks
- Film
- Fitness
- Food
- Spellen
- Gardening
- Health
- Home
- Literature
- Music
- Networking
- Overig
- Party
- Religion
- Shopping
- Sports
- Theater
- Wellness
 Dutch
 Indian
 English
 French
 Arabic
 Spanish
 Portuguese
 Deutsch
 Turkish
 Italiano
 Russian
 Romaian
 Portuguese (Brazil)
 Greek
